OPAL VS. C1 (CONDUCTORONE)
The C1 alternative that stays independent.
Workday has announced plans to acquire C1 (formerly ConductorOne) and build it into the Workday platform. Opal is an independent access governance platform for people and AI agents, with enforcement in the infrastructure you already run.
Trusted by leading companies


THE SHORT VERSION
Compare the approach.
How Opal and C1 compare on focus, independence, AI agents, and core access governance. C1 details reflect its public announcements as of October 2026.
What matters
Opal
C1
Built for access governance
OPAL
Purpose-built for access. Every product, from just-in-time access to Opal Zero, decides and enforces who gets access to what, for people and AI agents.
C1
Now splitting focus across app hosting, a secrets vault, an egress proxy, and an LLM gateway, with at least nine launches since March 2026.
Neutral to your HR system
OPAL
Independent of any HR vendor. Uses Workday or your identity provider as the source of truth, so access follows hires, moves, and exits.
C1
Workday plans to build C1 into its Agent System of Record. The deal is expected to close by January 31, 2027.
Governs AI agents in your gateway
OPAL
Opal Zero decides each agent request and enforces it in the gateway and identity provider you already run, without adding a new gateway.
C1
Offers its own MCP gateway, which routes agent tool calls through C1.
Just-in-time access beyond SaaS
OPAL
Time-limited access across cloud and infrastructure, including AWS, GCP, Azure, Kubernetes, Databricks, and Snowflake, removed automatically when the window ends.
C1
Just-in-time access requests, focused mainly on SaaS apps. Ask to see cloud access granted for an hour and removed on its own.
Access reviews anyone can finish
OPAL
AI recommends each decision with supporting evidence, and a person makes the final call.
C1
Offers review campaigns. Test them with a non-technical reviewer, not just an admin.
Policy as code
OPAL
OpalScript makes access policy version-controlled, PR-reviewed, and testable, like the rest of your infrastructure.
C1
Offers APIs and a CLI, with policy change history added in September 2026.
Fixes the cause, not just the finding
OPAL
Rotates or revokes risky service accounts, and Policy Insights turns repeat findings into one policy change.
C1
Routes findings to owners and ticketing tools.
In production.

Chronosphere
REDUCTION IN STANDING ACCESS
Permissions expire by default, so the attack surface shrinks on its own.
" transform="translate(2.666 1.334)" width="10.666680000000001px"/></svg>)
Security engineering
Superhuman
APPS UNDER GOVERNANCE
Lower access risk without slowing anyone down.
" transform="translate(2 7.334)" width="12px"/><path d="M 0 6 L 0 3.333 C 0 2.449 0.351 1.601 0.976 0.976 C 1.601 0.351 2.449 0 3.333 0 C 4.217 0 5.065 0.351 5.69 0.976 C 6.315 1.601 6.667 2.449 6.667 3.333 L 6.667 6" fill="transparent" height="6px" id="fztNhD33u" stroke-dasharray="" stroke-linecap="square" stroke-linejoin="round" stroke-width="1.33333" stroke="rgb(255, 255, 255)" transform="translate(4.666 1.334)" width="6.666680000000001px"/></svg>)
Platform
Mercari
OKTA ENTITLEMENTS GOVERNED
Automated reviews that surface real risk, not rubber-stamps.
" transform="translate(8 0.666)" width="1px"/><path d="M 7.333 0 L 2.333 0 C 1.714 0 1.121 0.246 0.683 0.683 C 0.246 1.121 0 1.714 0 2.333 C 0 2.952 0.246 3.546 0.683 3.983 C 1.121 4.421 1.714 4.667 2.333 4.667 L 5.667 4.667 C 6.286 4.667 6.879 4.912 7.317 5.35 C 7.754 5.788 8 6.381 8 7 C 8 7.619 7.754 8.212 7.317 8.65 C 6.879 9.088 6.286 9.333 5.667 9.333 L 0 9.333" fill="transparent" height="9.333319999999999px" id="qLYsPGXgK" stroke-dasharray="" stroke-linecap="butt" stroke-linejoin="round" stroke-width="1.33333" stroke="rgb(255, 255, 255)" transform="translate(4 3.334)" width="8px"/></svg>)
Compliance
Databricks
JUST-IN-TIME ACCESS REQUESTS
Every request handled by policy, no ticket queue required.
" transform="translate(1.334 1.33)" width="13.333311084581034px"/><path d="M 8.667 0 L 2 6.673 L 0 4.673" fill="transparent" height="6.67333px" id="idsX0jB3e" stroke-dasharray="" stroke-linecap="square" stroke-linejoin="miter" stroke-miterlimit="10" stroke-width="1.33333" stroke="rgb(255, 255, 255)" transform="translate(6 2.666)" width="8.6667px"/></g></svg>)
Identity & access
0
4
Keep access under your control.
Keep your gateway.
Opal Zero writes scoped, time-bound policy into the gateway you already run.
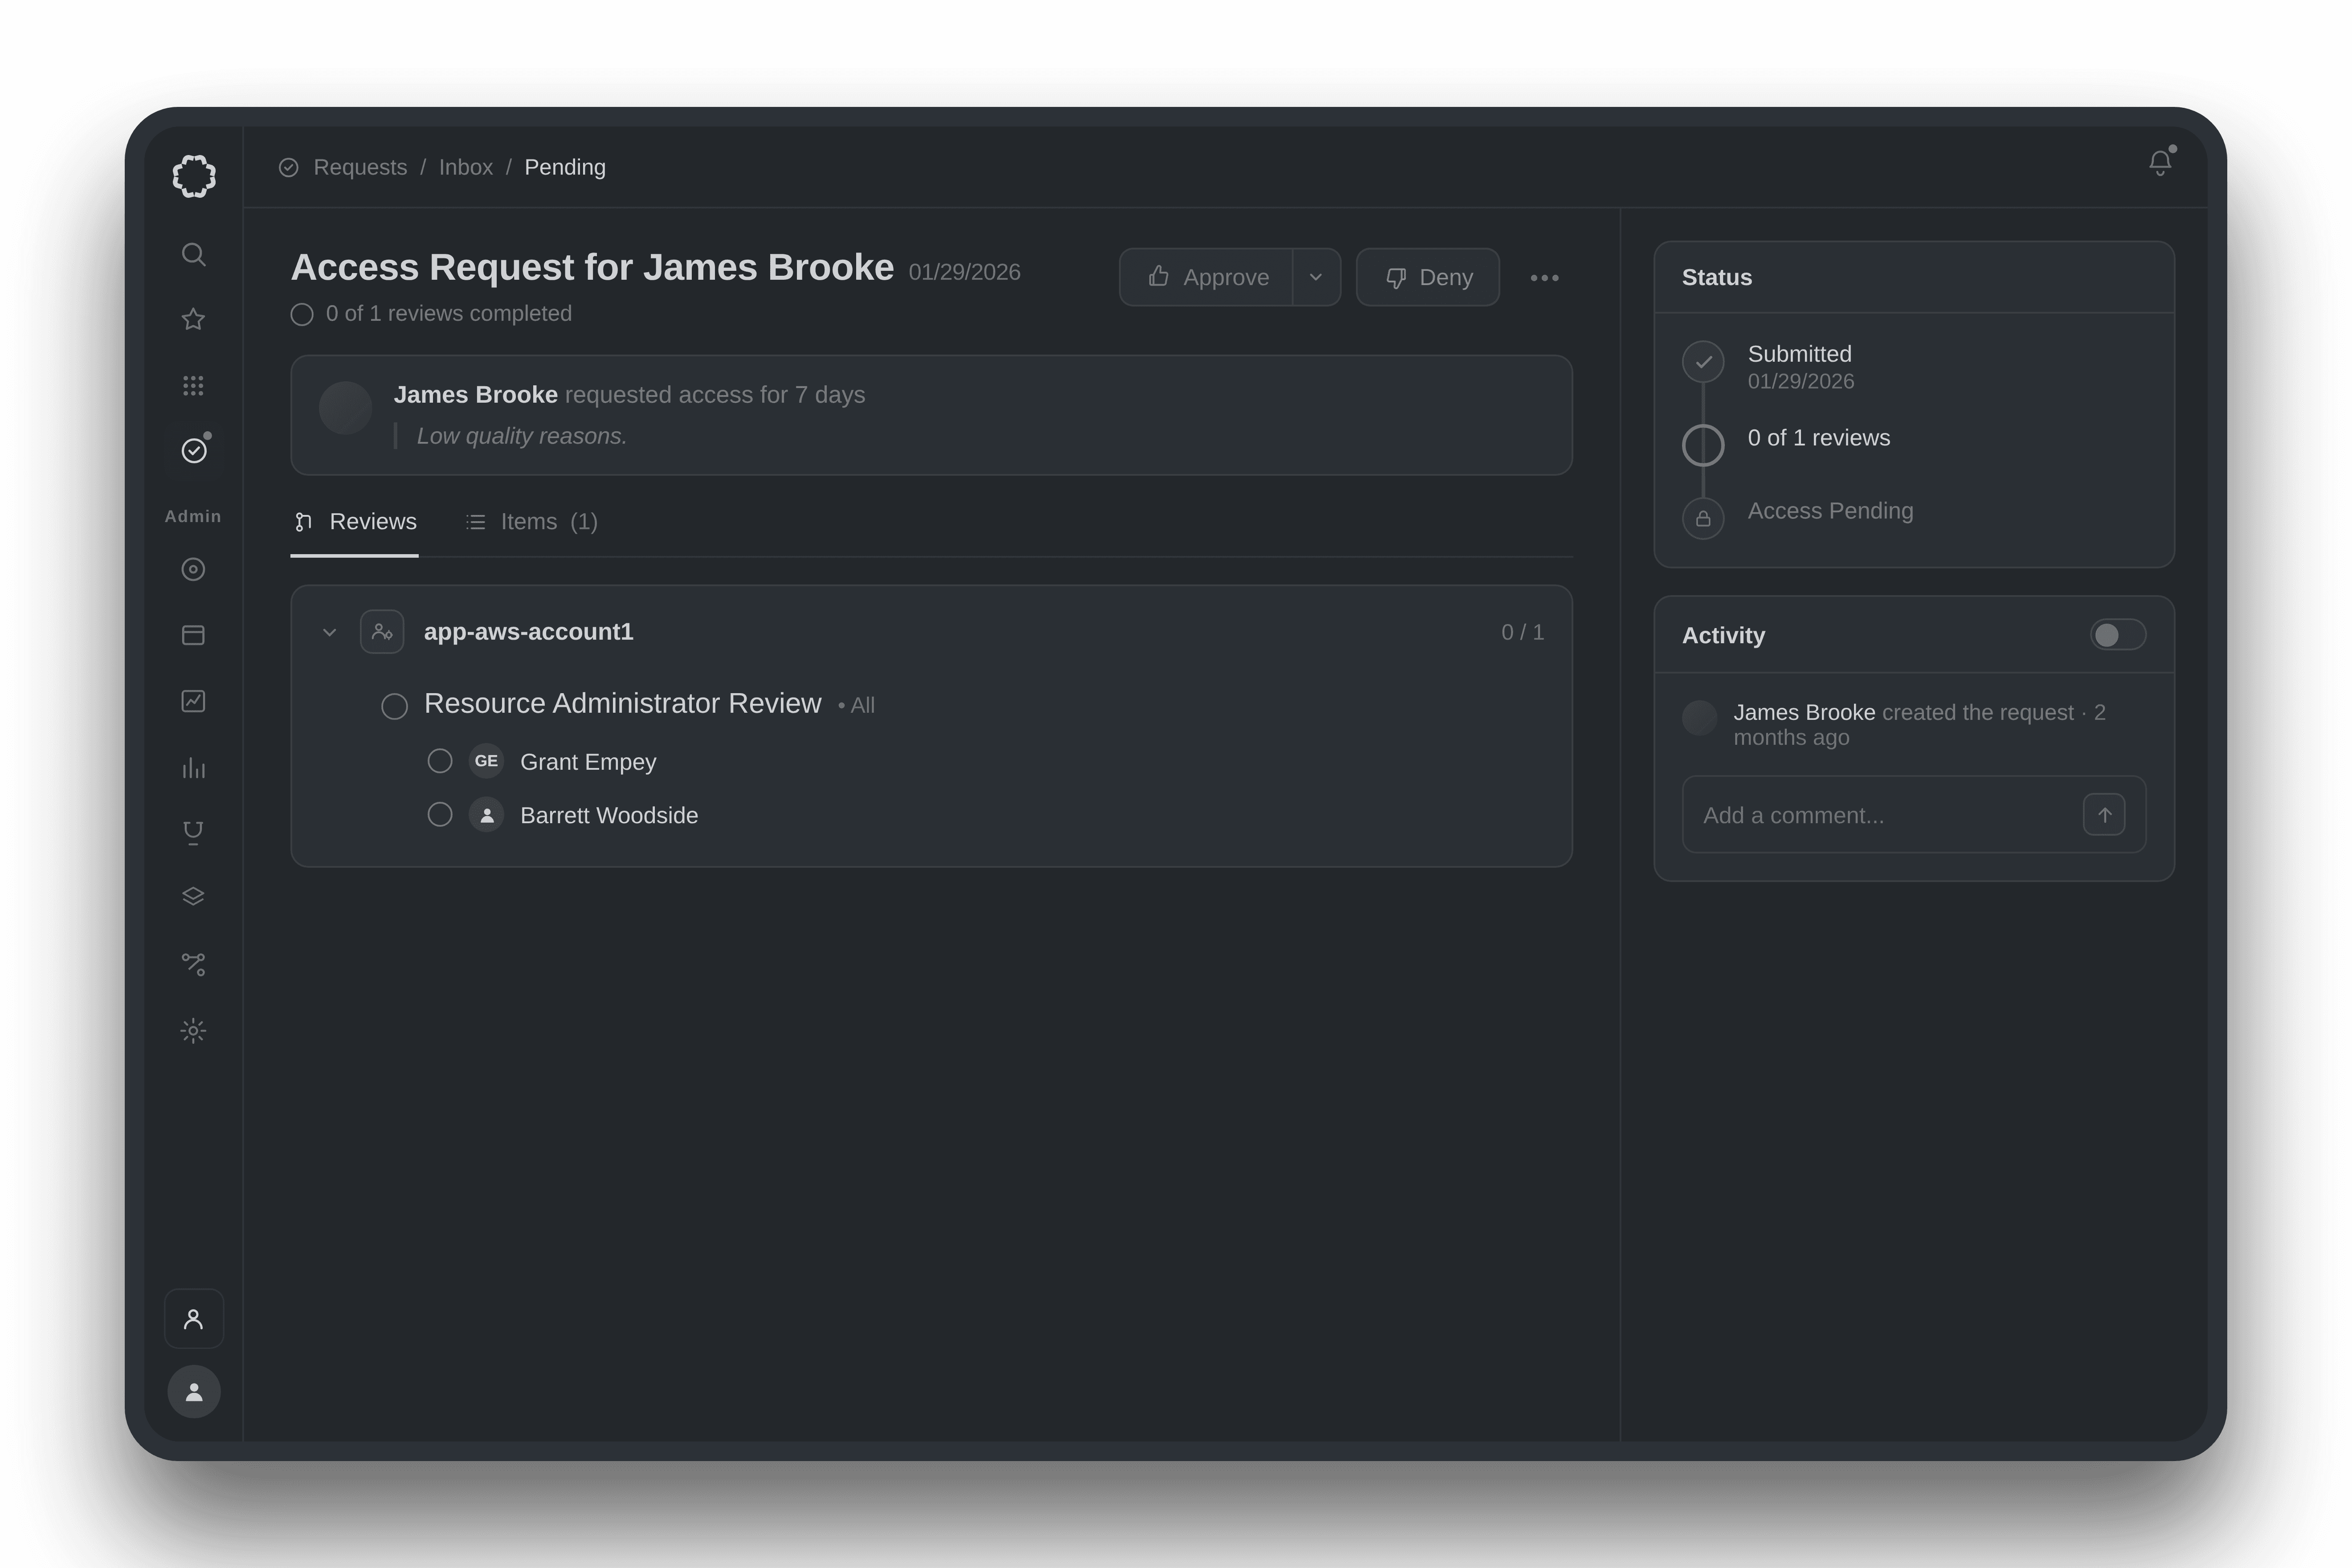
Grant access. Then remove it.
Give people time-limited access to cloud and infrastructure, with automatic revocation when the window ends.
Manage policy as code.
Use OpalScript to make access policy version-controlled and testable.
“By utilizing Opal’s extensive APIs, our IT and Infrastructure teams have been able to stay on top of the needs of our end users and empower them to gain Just-in-Time (JIT) Access, Just Enough Access (JEA), and enforce Time Bound Access Controls (TBAC) for security and compliance.”
Jack Zaldivar, Jr. · Staff Systems Engineer, Databricks
Databricks
Before your demo.
Is Opal an alternative to C1 (ConductorOne)?
What happens to C1 after the Workday acquisition?
What should I compare when evaluating C1 and Opal?
Does Opal Zero replace my MCP gateway?
How does Opal govern AI agents?
Does Opal work with Workday?
I just renewed with C1. Should I look now?
Ready to see it on your stack?
Bring your IdP, your cloud accounts, and your gateway. We’ll show you a real request, the decision, and where it lands.
OPAL VS. C1 (CONDUCTORONE)
The C1 alternative that stays independent.
Workday has announced plans to acquire C1 (formerly ConductorOne) and build it into the Workday platform. Opal is an independent access governance platform for people and AI agents, with enforcement in the infrastructure you already run.
Trusted by leading companies
THE SHORT VERSION
Compare the approach.
How Opal and C1 compare on focus, independence, AI agents, and core access governance. C1 details reflect its public announcements as of October 2026.
What matters
Opal
C1
Built for access governance
OPAL
Purpose-built for access. Every product, from just-in-time access to Opal Zero, decides and enforces who gets access to what, for people and AI agents.
C1
Now splitting focus across app hosting, a secrets vault, an egress proxy, and an LLM gateway, with at least nine launches since March 2026.
Neutral to your HR system
OPAL
Independent of any HR vendor. Uses Workday or your identity provider as the source of truth, so access follows hires, moves, and exits.
C1
Workday plans to build C1 into its Agent System of Record. The deal is expected to close by January 31, 2027.
Governs AI agents in your gateway
OPAL
Opal Zero decides each agent request and enforces it in the gateway and identity provider you already run, without adding a new gateway.
C1
Offers its own MCP gateway, which routes agent tool calls through C1.
Just-in-time access beyond SaaS
OPAL
Time-limited access across cloud and infrastructure, including AWS, GCP, Azure, Kubernetes, Databricks, and Snowflake, removed automatically when the window ends.
C1
Just-in-time access requests, focused mainly on SaaS apps. Ask to see cloud access granted for an hour and removed on its own.
Access reviews anyone can finish
OPAL
AI recommends each decision with supporting evidence, and a person makes the final call.
C1
Offers review campaigns. Test them with a non-technical reviewer, not just an admin.
Policy as code
OPAL
OpalScript makes access policy version-controlled, PR-reviewed, and testable, like the rest of your infrastructure.
C1
Offers APIs and a CLI, with policy change history added in September 2026.
Fixes the cause, not just the finding
OPAL
Rotates or revokes risky service accounts, and Policy Insights turns repeat findings into one policy change.
C1
Routes findings to owners and ticketing tools.
In production.
Chronosphere
REDUCTION IN STANDING ACCESS
Permissions expire by default, so the attack surface shrinks on its own.
Security engineering
Superhuman
APPS UNDER GOVERNANCE
Lower access risk without slowing anyone down.
Platform
Mercari
OKTA ENTITLEMENTS GOVERNED
Automated reviews that surface real risk, not rubber-stamps.
Compliance
Databricks
JUST-IN-TIME ACCESS REQUESTS
Every request handled by policy, no ticket queue required.
Identity & access
0
4
Keep access under your control.
Keep your gateway.
Opal Zero writes scoped, time-bound policy into the gateway you already run.
Grant access. Then remove it.
Give people time-limited access to cloud and infrastructure, with automatic revocation when the window ends.
Manage policy as code.
Use OpalScript to make access policy version-controlled and testable.
“By utilizing Opal’s extensive APIs, our IT and Infrastructure teams have been able to stay on top of the needs of our end users and empower them to gain Just-in-Time (JIT) Access, Just Enough Access (JEA), and enforce Time Bound Access Controls (TBAC) for security and compliance.”
Jack Zaldivar, Jr. · Staff Systems Engineer, Databricks
Databricks
Before your demo.
Is Opal an alternative to C1 (ConductorOne)?
What happens to C1 after the Workday acquisition?
What should I compare when evaluating C1 and Opal?
Does Opal Zero replace my MCP gateway?
How does Opal govern AI agents?
Does Opal work with Workday?
I just renewed with C1. Should I look now?
Ready to see it on your stack?
Bring your IdP, your cloud accounts, and your gateway. We’ll show you a real request, the decision, and where it lands.